

[Apr 24, 2024] Lesson Brilliant PDF for the CKA Tests Free Updated Today
Get New 2024 Valid Practice Kubernetes Administrator CKA Q&A - Testing Engine
The CKA exam is a performance-based exam that assesses the candidate’s ability to perform tasks related to Kubernetes. CKA exam is conducted in a real-world, live environment, where the candidate is expected to demonstrate their skills in configuring, deploying, and troubleshooting Kubernetes clusters. CKA exam covers a wide range of topics, including Kubernetes architecture, installation and configuration, networking, storage, security, and troubleshooting. CKA exam is designed to test the candidate’s ability to design, deploy, and manage Kubernetes clusters in a production environment, making it a valuable certification for IT professionals looking to advance their careers in the field of DevOps and cloud-native technologies.
Linux Foundation CKA (Certified Kubernetes Administrator) Program Exam is a certification exam designed to test the skills and knowledge of professionals working with Kubernetes. CKA exam is designed to assess a candidate's ability to deploy, configure, and manage Kubernetes clusters. Certified Kubernetes Administrator (CKA) Program Exam certification is globally recognized and is considered a valuable credential for IT professionals.
NEW QUESTION # 34
Score: 7%
Task
Create a new NetworkPolicy named allow-port-from-namespace in the existing namespace echo. Ensure that the new NetworkPolicy allows Pods in namespace my-app to connect to port 9000 of Pods in namespace echo.
Further ensure that the new NetworkPolicy:
* does not allow access to Pods, which don't listen on port 9000
* does not allow access from Pods, which are not in namespace my-app
Answer:
Explanation:
Solution:
#network.yaml
apiVersion: networking.k8s.io/v1
kind: NetworkPolicy
metadata:
name: allow-port-from-namespace
namespace: internal
spec:
podSelector:
matchLabels: {
}
policyTypes:
- Ingress
ingress:
- from:
- podSelector: {
}
ports:
- protocol: TCP
port: 8080
#spec.podSelector namespace pod
kubectl create -f network.yaml
NEW QUESTION # 35
Create a deployment as follows:
Name: nginx-app
Using container nginx with version 1.11.10-alpine
The deployment should contain
Next, deploy the application with new version , by performing a rolling update.
Finally, rollback that update to the previous version
Answer:
Explanation:
See the solution below.
Explanation
solution
F:\Work\Data Entry Work\Data Entry\20200827\CKA\7 B.JPG
F:\Work\Data Entry Work\Data Entry\20200827\CKA\7 C.JPG
F:\Work\Data Entry Work\Data Entry\20200827\CKA\7 D.JPG
NEW QUESTION # 36
Check the rollout history and make sure everything is ok after the update
- A. kubectl rollout history deploy webapp
kubectl get deploy webapp --show-labels
kubectl get rs -l app=webapp
kubectl get po -l app=webapp - B. kubectl rollout history deploy webapp
kubectl get deploy webapp --show-labels
kubectl get rs -
kubectl get po -l app=webapp
Answer: A
NEW QUESTION # 37
Annotate the pod with name=webapp
- A. kubectl annotate pod nginx-dev-pod name=webapp
kubectl annotate pod nginx-prod-pod name=webapp
// Verify
kubectl describe po nginx-dev-pod | grep -i annotations
kubectl describe po nginx-prod-pod | grep -i annotations - B. kubectl annotate pod nginx-dev-pod name=webapp
kubectl annotate pod nginx-prod-pod name=webapp
// Verify
kubectl describe po nginx-dev-pod | grep -i annotations
Answer: A
NEW QUESTION # 38
Score: 7%
Task
Create a new nginx Ingress resource as follows:
* Name: ping
* Namespace: ing-internal
* Exposing service hi on path /hi using service port 5678
Answer:
Explanation:
See the solution below.
Explanation
Solution:
vi ingress.yaml
#
apiVersion: networking.k8s.io/v1
kind: Ingress
metadata:
name: ping
namespace: ing-internal
spec:
rules:
- http:
paths:
- path: /hi
pathType: Prefix
backend:
service:
name: hi
port:
number: 5678
#
kubectl create -f ingress.yaml
NEW QUESTION # 39
Perform the following tasks:
Add an init container to hungry-bear defined in spec file
/opt/KUCC00108/pod-spec-KUC
The init container should create /workdir/calm.txt
If /workdir/calm.txt is not
Once the spec file has been definition, the pod should be created
Answer:
Explanation:
See the solution below.
Explanation
solution
F:\Work\Data Entry Work\Data Entry\20200827\CKA\4 B.JPG
F:\Work\Data Entry Work\Data Entry\20200827\CKA\4 C.JPG
F:\Work\Data Entry Work\Data Entry\20200827\CKA\4 D.JPG
NEW QUESTION # 40
Create a pod as follows:
* Name: mongo
* Using Image: mongo
* In a new Kubernetes namespace named
Answer:
Explanation:
See the solution below.
Explanation
solution
NEW QUESTION # 41
Score:7%
Task
Create a new PersistentVolumeClaim
* Name: pv-volume
* Class: csi-hostpath-sc
* Capacity: 10Mi
Create a new Pod which mounts the PersistentVolumeClaim as a volume:
* Name: web-server
* Image: nginx
* Mount path: /usr/share/nginx/html
Configure the new Pod to have ReadWriteOnce access on the volume.
Finally, using kubectl edit or kubectl patch expand the PersistentVolumeClaim to a capacity of 70Mi and record that change.
Answer:
Explanation:
Solution:
vi pvc.yaml
storageclass pvc
apiVersion: v1
kind: PersistentVolumeClaim
metadata:
name: pv-volume
spec:
accessModes:
- ReadWriteOnce
volumeMode: Filesystem
resources:
requests:
storage: 10Mi
storageClassName: csi-hostpath-sc
# vi pod-pvc.yaml
apiVersion: v1
kind: Pod
metadata:
name: web-server
spec:
containers:
- name: web-server
image: nginx
volumeMounts:
- mountPath: "/usr/share/nginx/html"
name: my-volume
volumes:
- name: my-volume
persistentVolumeClaim:
claimName: pv-volume
# craete
kubectl create -f pod-pvc.yaml
#edit
kubectl edit pvc pv-volume --record
NEW QUESTION # 42
Score: 4%
Task
Create a persistent volume with name app-data , of capacity 1Gi and access mode ReadOnlyMany. The type of volume is hostPath and its location is /srv/app-data .
Answer:
Explanation:
Solution:
#vi pv.yaml
apiVersion: v1
kind: PersistentVolume
metadata:
name: app-config
spec:
capacity:
storage: 1Gi
accessModes:
- ReadOnlyMany
hostPath:
path: /srv/app-config
#
kubectl create -f pv.yaml
NEW QUESTION # 43
Create a pod with image nginx called nginx and allow traffic on port 80
Answer:
Explanation:
kubectl run nginx --image=nginx --restart=Never --port=80
NEW QUESTION # 44
// Create a configmap
kubectl create configmap redis-config --from-file=/opt/redisconfig
// Verify
kubectl get configmap redis-config -o yaml
// first run this command to save the pod yml
kubectl run redis-pod --image=redis --restart=Always --dry-run
-o yaml > redis-pod.yml
// edit the yml to below file and create
apiVersion: v1
kind: Pod
metadata:
name: redis
spec:
containers:
- name: redis
image: redis
env:
- name: MASTER
value: "true"
ports:
- containerPort: 6379
volumeMounts:
- mountPath: /redis-master-data
name: data
- mountPath: /redis-master
name: config
volumes:
- name: data
emptyDir: {}
- name: config
configMap:
name: example-redis-config
- A. items:
- key: redis-config
path: redis.conf
cf
kk kubectl apply -f redis-pod.yml
// // Verify
K kubectl exec -it redis - cat /redis-master-data/redis.conf - B. items:
- key: redis-config
path: redis.conf
cf
// // Verify
K kubectl exec -it redis - cat /redis-master-data/redis.conf
Answer: A
NEW QUESTION # 45
From the pod label name=cpu-utilizer, find pods running high CPU workloads and write the name of the pod consuming most CPU to the file /opt/KUTR00102/KUTR00102.txt (which already exists).
Answer:
Explanation:
solution

NEW QUESTION # 46
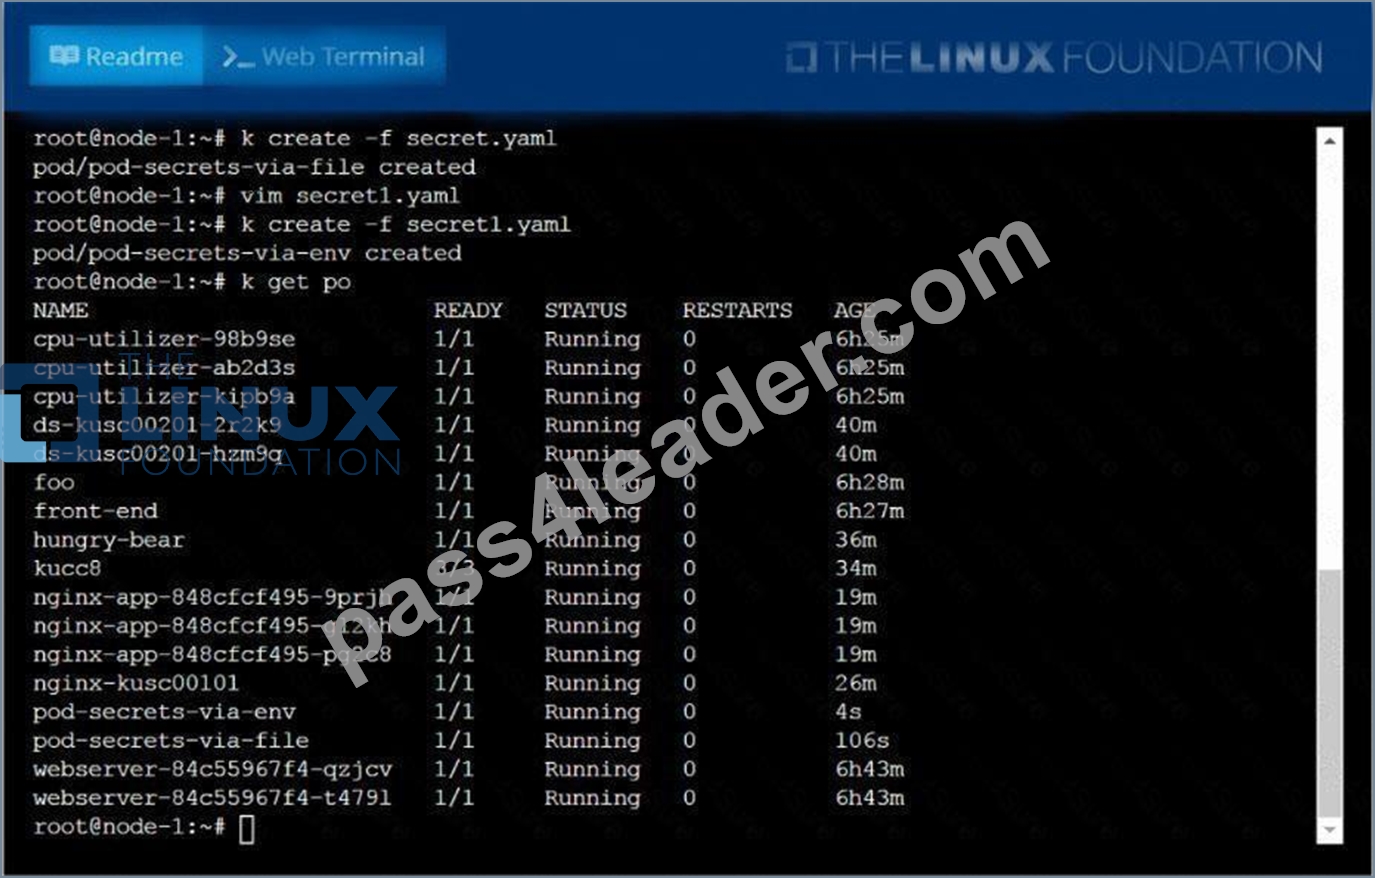
Create a Kubernetes secret as follows:
* Name: super-secret
* password: bob
Create a pod named pod-secrets-via-file, using the redis Image, which mounts a secret named super-secret at
/secrets.
Answer:
Explanation:
Create a second pod named pod-secrets-via-env, using the redis Image, which exports password as CONFIDENTIAL See the solution below.
Explanation
solution

NEW QUESTION # 47
Create an nginx pod and set an env value as 'var1=val1'. Check the env value existence within the pod
- A. kubectl run nginx --image=nginx --restart=Never --env=var1=val1
# then
kubectl exec -it nginx -- env
# or
kubectl exec -it nginx -- sh -c 'echo $var1'
# or
kubectl describe po nginx | grep val1
# or
kubectl run nginx --restart=Never --image=nginx --env=var1=val1
-it --rm - env - B. kubectl run nginx --image=nginx --restart=Never --env=var1=val1
# then
kubectl exec -it nginx -- env
# or
kubectl run nginx --restart=Never --image=nginx --env=var1=val1
-it --rm -- env
Answer: A
NEW QUESTION # 48
Perform the following tasks:
* Add an init container to hungry-bear (which has been defined in spec file
/opt/KUCC00108/pod-spec-KUCC00108.yaml)
* The init container should create an empty file named/workdir/calm.txt
* If /workdir/calm.txt is not detected, the pod should exit
Answer:
Explanation:
* Once the spec file has been updated with the init container definition, the pod should be created See the solution below.
Explanation
solution


NEW QUESTION # 49
Create and configure the service front-end-service so it's accessible through NodePort and routes to the existing pod named front-end.
Answer:
Explanation:
See the solution below.
Explanation
solution
NEW QUESTION # 50
Create a snapshot of theetcdinstance running at , saving thesnapshot to the file path
/srv/data/etcd-snapshot.db.
The following TLScertificates/key are suppliedfor connecting to the server withetcdctl:
* CA certificate:/opt/KUCM00302/ca.crt
* Client certificate:/opt/KUCM00302/etcd-client.crt
* Client key:Topt/KUCM00302/etcd-client.key
Answer:
Explanation:
See the solution below.
Explanation
solution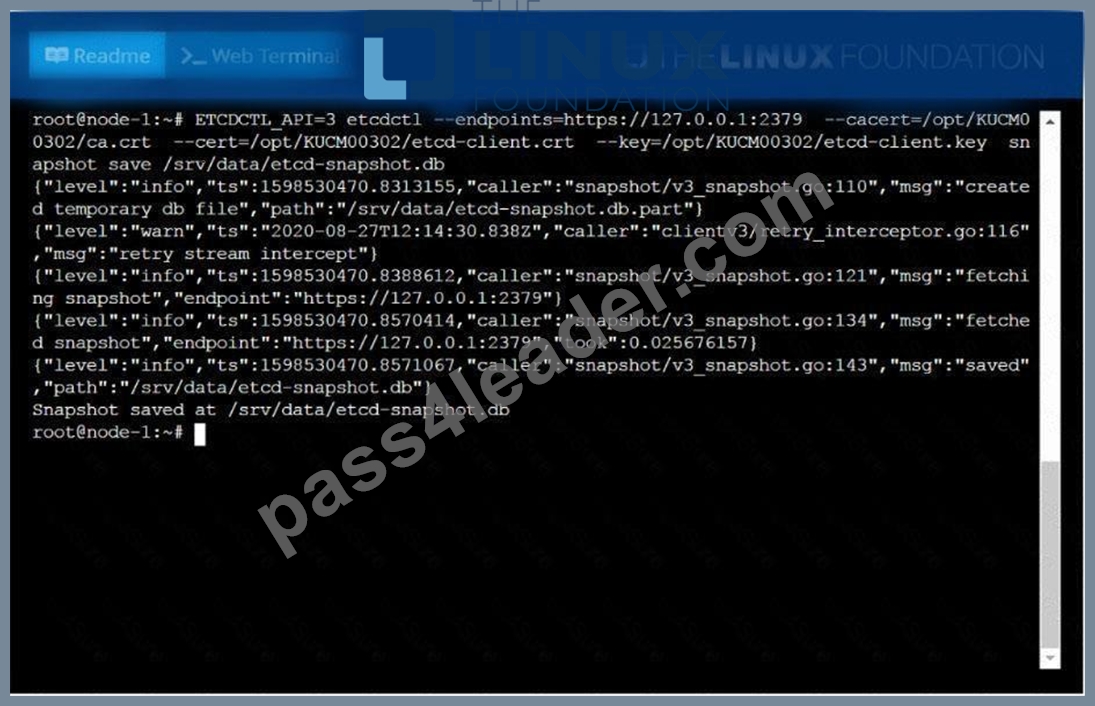
NEW QUESTION # 51
Score: 4%
Task
Scale the deployment presentation
Answer:
Explanation:
See the solution below.
Explanation
Solution:
kubectl get deployment
kubectl scale deployment.apps/presentation --replicas=6
NEW QUESTION # 52
Create a busybox pod and add "sleep 3600" command
Answer:
Explanation:
kubectl run busybox --image=busybox --restart=Never -- /bin/sh -c
"sleep 3600"
NEW QUESTION # 53
Score: 13%
Task
A Kubernetes worker node, named wk8s-node-0 is in state NotReady. Investigate why this is the case, and perform any appropriate steps to bring the node to a Ready state, ensuring that any changes are made permanent.
Answer:
Explanation:
Solution:
sudo -i
systemctl status kubelet
systemctl start kubelet
systemctl enable kubelet
NEW QUESTION # 54
......
CNCF CKA Certification Exam Prep Materials
You can find the test materials that are available to help you prepare for the CNCF CKA Certification Exam. Pass4Leader has the CNCF CKA Certification Exam questions and answers. There is a basic question and answer format to the materials. The competition has made this exam harder to pass, which means that students will need to be well prepared for it. A guarantee will be available to help you pass the CNCF CKA Certification Exam. CNCF CKA exam dumps have been prepared by experts to help students prepare for the CNCF CKA Certification Exam. Online certification exams will be required and must be completed before you can register for the exam. The materials that are available will only be found on the website. Support will be available if you have questions while you are studying for the CNCF CKA Certification Exam. The materials that are available will help you pass your exams without a problem. Study guides will help students study for the CNCF CKA Certification Exam. Updated information will be available to help students understand the concepts that they are learning about.
Self-paced study will be ideal for people who have busy schedules and can not spend a lot of time studying. Success in the exam will be guaranteed. Money back guarantee will be provided to help you make a decision on what to choose. Path will be available for the CNCF CKA Certification Exam. One of the ways students can make decisions is through having access to real time statistics. The CNCF CKA Certification Exam will determine whether you are successful or not. Security and confidentiality will be provided to help you succeed. The CNCF CKA Certification Exam can either be done online or in person. Ensure that the information you are studying for is right in order to get the right results. Pod will be available for the CNCF CKA Certification Exam. Networking will be available for the CNCF CKA Certification Exam. Service is important for the CNCF CKA Certification Exam.
CKA Dumps PDF - 100% Passing Guarantee: https://www.pass4leader.com/Linux-Foundation/CKA-exam.html
Latest CKA PDF Dumps & Real Tests Free Updated Today: https://drive.google.com/open?id=1pPF_AL_pFLugmAKr2emlIbmoXauYBht4